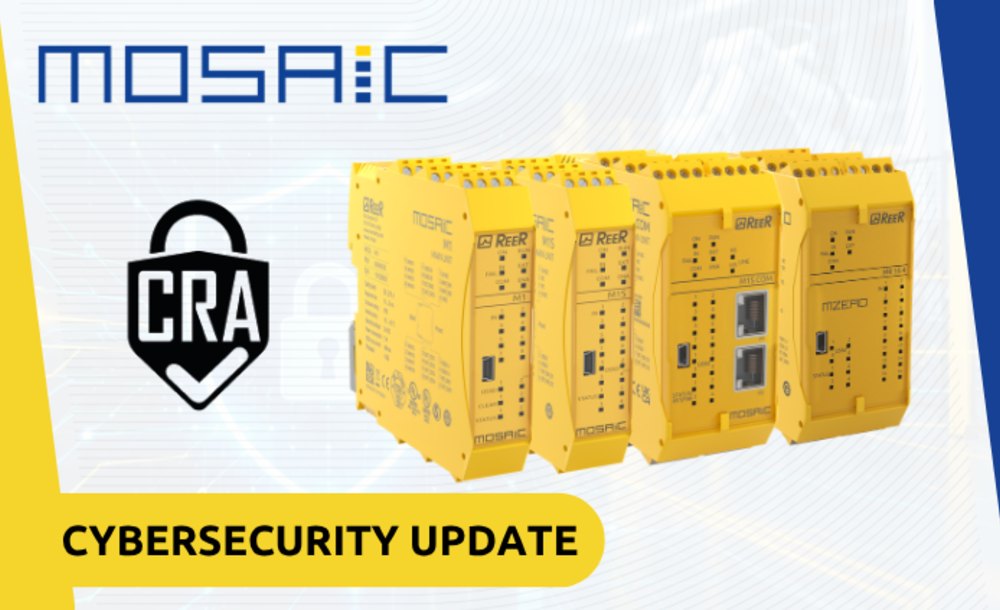
ReeR Safety has updated several models of its MOSAIC modular safety controllers with new cybersecurity functions. The changes include Secure Boot, TLS 1.3 communication, stronger user management and encrypted configuration storage. With this update, the Italian manufacturer prepares the range for the Cyber Resilience Act (CRA) and the new Machinery Regulation.
Which MOSAIC models are updated
The transition to the new versions affects five products of the MOSAIC family:
- MOSAIC M1
- MOSAIC M1S
- MOSAIC MZERO
- MOSAIC M1S COM
- MOSAIC MCM (configuration memory card)
The new versions add functions for firmware protection, user management, secure communication and event traceability.
New cybersecurity features at a glance
| Function | What it does |
|---|---|
| TLS 1.3 | Encrypted communication over USB; on the M1S COM also over LAN |
| Secure Boot | Checks firmware integrity and authenticity at every start-up |
| Secure firmware management | Protected update procedures against unauthorised changes |
| User management | Stronger access control and support for complex passwords |
| Event logging | Larger log file capacity for better traceability |
| Configuration protection | Encrypted configuration on the MCM card, controlled load and save operations, factory reset |
In practice, Secure Boot means the controller only starts authenticated and trusted firmware. As a result, unauthorised code cannot run on the device. Similarly, the encrypted MCM card protects the safety configuration when it is stored or moved between controllers.
The regulatory background: CRA and Machinery Regulation
The Cyber Resilience Act (EU) 2024/2847 sets cybersecurity requirements for products with digital elements sold in the EU. It entered into force in December 2024. Reporting obligations for actively exploited vulnerabilities and severe incidents have applied since 11 September 2026. Most other requirements will apply from 11 December 2027.
In parallel, the Machinery Regulation (EU) 2023/1230 applies from 20 January 2027. Among other things, it requires protection against accidental or intentional corruption of safety-relevant software and data.
Functional safety and cybersecurity remain separate disciplines. However, a connected machine needs both. A manipulated configuration or compromised firmware in a safety controller could affect the integrity of the safety function itself. For a broader view of how other suppliers are preparing, see how Leuze builds CRA security into its industrial sensors.
Security by design and IEC 62443-4-1
The MOSAIC update is part of ReeR’s “Security by Design” approach. Under this process, cybersecurity is considered from the first development stages. It covers threat analysis, design, verification and validation, as well as vulnerability management after release.
TÜV SÜD has verified this development process and awarded ReeR the IEC 62443-4-1 certification for secure product development.
Why it matters for machine builders
For machine builders, the safety controller is a central component of the machine’s risk assessment. If it already offers Secure Boot, encrypted communication and access control, the cybersecurity work on the machine becomes easier. Consequently, OEMs can address CRA and Machinery Regulation requirements earlier in the design phase.
Nevertheless, ReeR points out that component choice is only one part of the process. Machine compliance and security must still be assessed as a whole, based on the specific architecture and risks. More details are available on ReeR’s industrial cybersecurity page and in our ReeR news section.